← Back to catalogue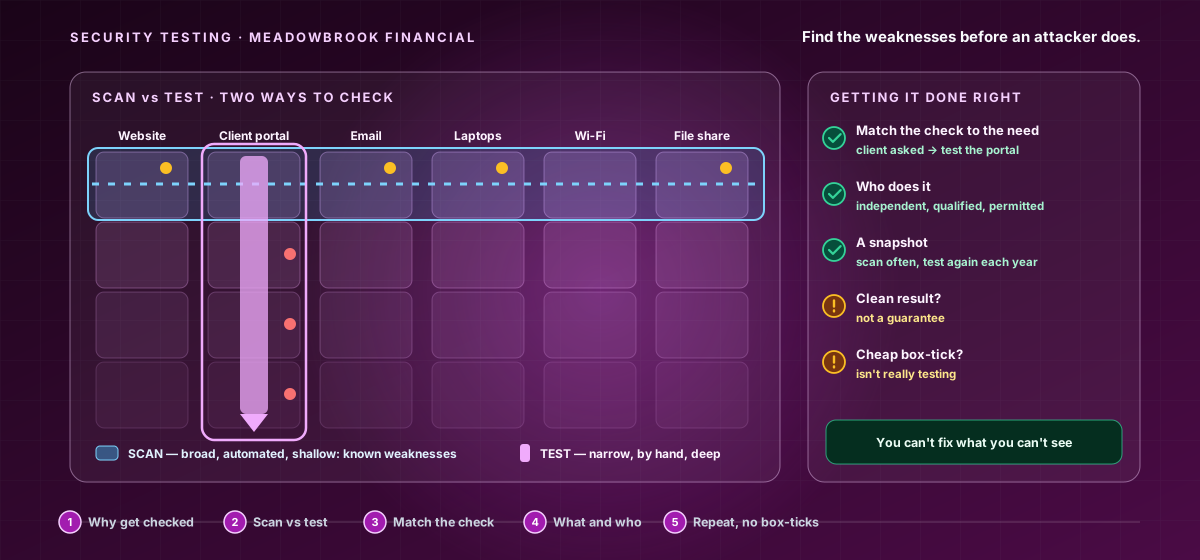
CY-BEGINNER-083Beginner · Vulnerability Assessment and Penetration Testing
The Check-Up — Getting Your Systems Tested for Weaknesses
You can't fix what you can't see, so a test finds your weaknesses before an attacker does. A scan is broad and shallow; a test is narrow and deep. Match the check to your need, test what matters, choose a good tester, repeat it, and act on what it finds.
11 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Understand that you can't fix what you can't see, and tell a broad, shallow scan from a narrow, deep penetration test.
- Match the check to what you want to find out, and scope the deep testing to what matters most.
- Choose a competent, trustworthy tester and authorise them clearly, and treat a test as a snapshot to repeat.
- Hold a clean result humbly — it isn't a guarantee — and get real value by insisting on scope, depth, and acting on what it finds.
Price:৳5,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.