← Back to catalogue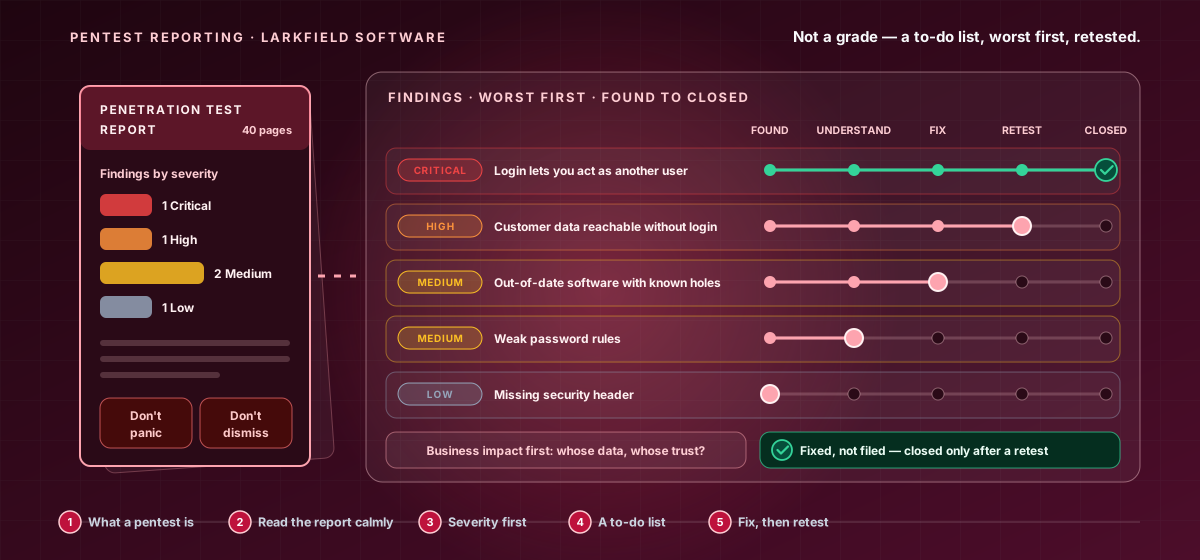
CY-BEGINNER-078Beginner · Penetration Testing Reporting
The Findings — Reading and Acting on a Penetration Test Report
A penetration test is a hired, ethical test that finds your weaknesses so you can fix them first. Its report is a to-do list, not a grade. Read it calmly for impact, fix the worst first by severity, and confirm your fixes with a retest.
11 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Understand a penetration test as a hired, ethical test on your side, and its report — not the test — as the to-do list you act on.
- React calmly rather than panicking or dismissing, using severity to fix the critical and high findings first.
- Read each finding for its business impact, and treat the report as a to-do list, not a grade to fear.
- Fix the findings rather than filing the report, and confirm your fixes with a retest.
Price:৳5,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.