← Back to catalogue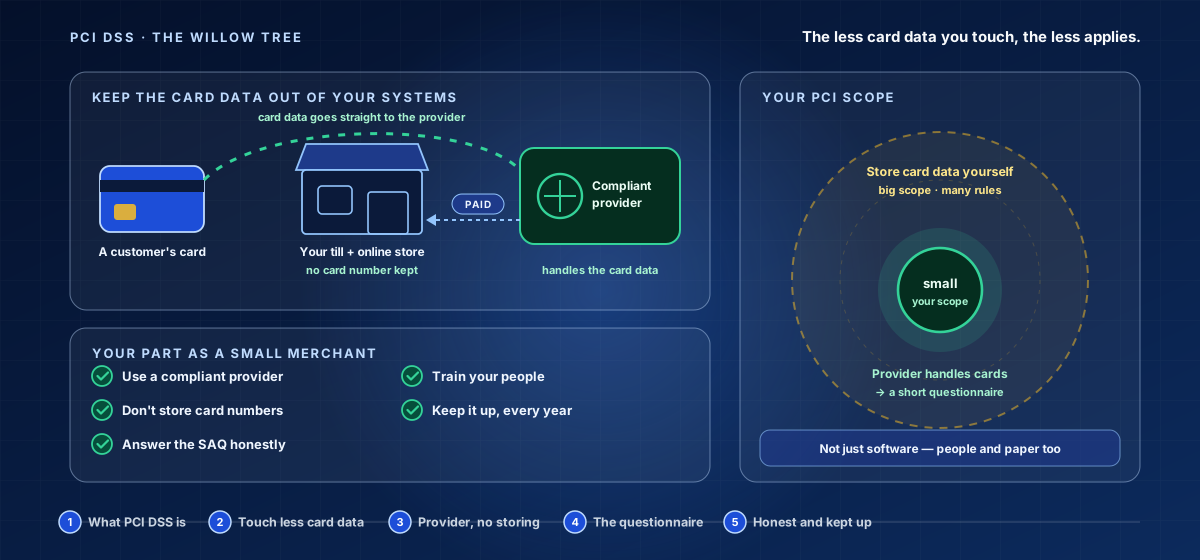
CY-BEGINNER-079Beginner · Payment Security and PCI DSS
The Scope — PCI DSS for a Small Merchant Taking Card Payments
PCI DSS is the set of rules for taking card payments safely. The key is scope: the less card data you touch, the less applies. Let a compliant provider handle the cards, never store the number, do the questionnaire honestly, mind the human side, and keep it up.
11 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Understand PCI DSS as the rules for taking card payments safely, and scope — that the less card data you touch, the less applies — as the key to making it manageable.
- Let a compliant provider handle the cards and never store the card number, keeping the card data and most of the burden away from you.
- Understand the self-assessment questionnaire, complete the right one honestly, and mind the human side of protecting card data.
- Answer the questionnaire honestly, fixing gaps rather than faking answers, and treat compliance as an ongoing practice kept up over time.
Price:৳5,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.