← Back to catalogue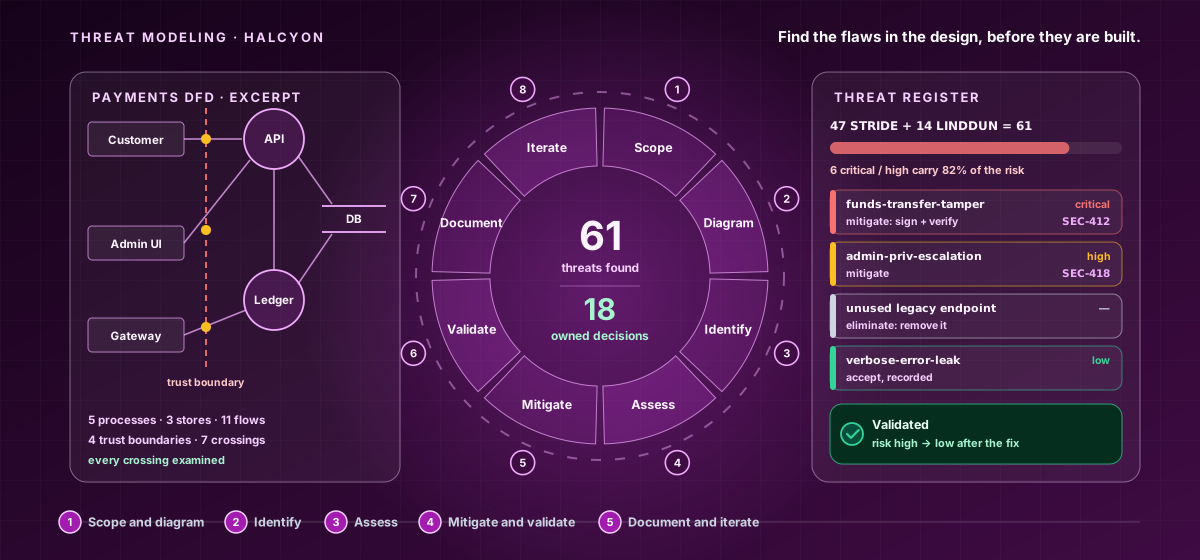
CY-MID-007Mid Level · Threat Modeling
Threat Modeling — The Threat Model Loop
A hands-on mid-level course that finds security problems in a design before they are built, by modeling the system and reasoning about what can go wrong. Work the threat model loop - eight stages a model cycles through: Scope, Diagram, Identify, Assess, Mitigate, Validate, Document, and Iterate - answering the four questions and ending in decisions, not a list, with real data flow diagrams, trust boundaries, STRIDE and LINDDUN enumeration, risk rating, and mitigation design. Four hands-on activities in every lesson.
15 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Scope and diagram a system as data flows with trust boundaries.
- Identify threats systematically with STRIDE, attacker reasoning, and LINDDUN.
- Assess threats by realistic risk and decide and design mitigations in.
- Validate the model, document it actionably, and keep it living in the SDLC.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.