← Back to catalogue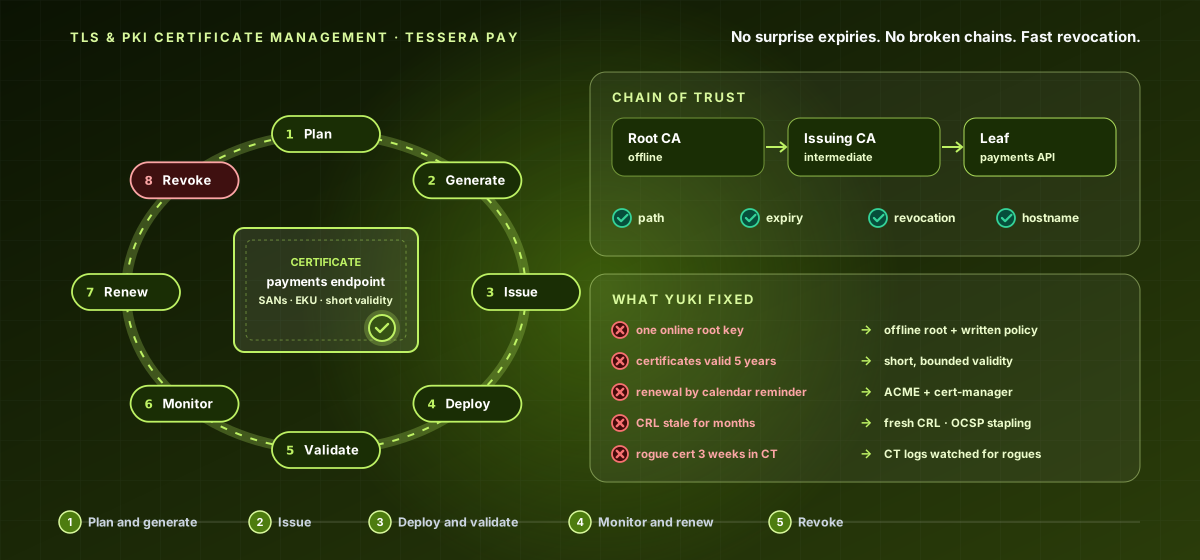
CY-MID-040Mid Level · PKI & Certificates
TLS & PKI Certificate Management — The Certificate Lifecycle
A hands-on mid-level course that runs certificates and trust without outages or weak crypto. Climb the certificate lifecycle - eight steps: Plan, Generate, Issue, Deploy, Validate, Monitor, Renew, and Revoke - building a CA hierarchy, strong TLS, automated renewal, and revocation with real OpenSSL and ACME work. Strictly defensive. Four hands-on activities in every lesson.
15 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Design a CA hierarchy and generate keys and CSRs correctly.
- Issue and deploy certificates with strong TLS configuration.
- Validate chains, monitor expiry, and automate renewal with ACME.
- Revoke compromised certificates and manage trust stores.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.