← Back to catalogue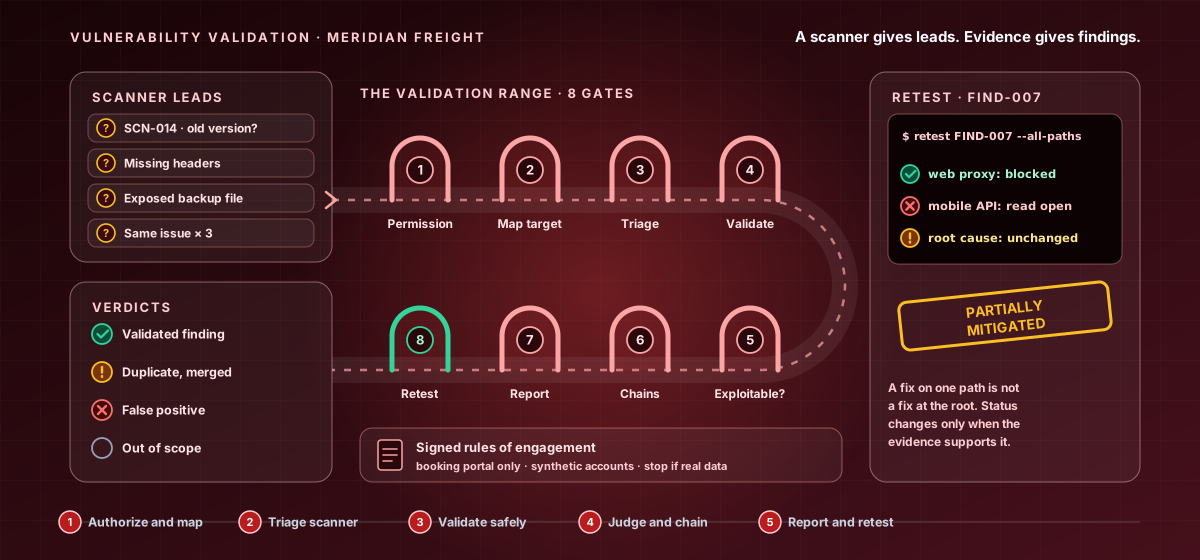
CY-BEGINNER-003Beginner · VAPT
Vulnerability Validation Range — From Scanner Finding to Exploitability Decision
A nine-hour authorized technical range where you scope safely, interrogate scanner output, validate with minimum proof, rate exploitability, model attack paths, write findings, and defend retest conclusions.
9 hours8 chapters32 lessons100 activities8 labs
What you'll learn
- Write executable rules of engagement with proof limits and stop conditions.
- Turn scanner leads into safe, reproducible manual validation.
- Separate severity, exploitability, controls, impact, and evidence confidence.
- Write and retest professional findings without exceeding authorization.
Price:৳5,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.