← Back to catalogue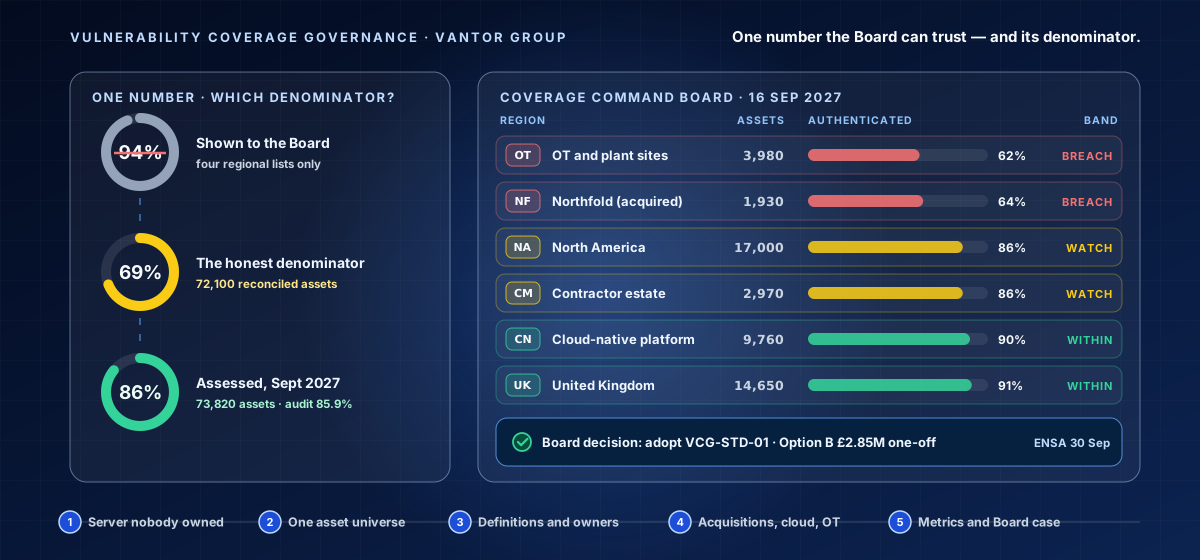
CY-PRO-009Pro Level · Vulnerability Management
Vulnerability Coverage Governance
A forty-hour Pro-level coverage-command simulation run on a live vulnerability coverage command board, where you are Group Head of Vulnerability Management at a multinational energy-infrastructure group built by acquisition — every region with its own scanner, its own ‘critical’ and its own asset list — after a breach through an unscanned server in an acquired company's cloud account that no region believed it owned; the regulator demands proof of group-wide coverage, the Board demands one number it can trust, and you rebuild coverage governance end to end, price it and defend it to the Board as one decision.
40 hours12 chapters60 lessons433 activities12 labs
What you'll learn
- Reconcile regional and platform inventories into one asset universe with an honest denominator, and define coverage tiers and measurement rules that an independent party can recompute.
- Assign ownership by rule across a hub-and-spoke model, and extend coverage to acquisitions, cloud and ephemeral workloads, OT, supplier-managed and unmanaged estates with methods fit for each.
- Harmonise severity into a group priority model with SLAs measured from first detection, and govern exceptions and compensating controls against the Board's risk appetite.
- Choose a headline metric with companions, bridges, lineage and guards, price the programme at the margin with residual risk stated for its proper owner, and win a Board resolution that names the control owner.
Price:৳15,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.