← Back to catalogue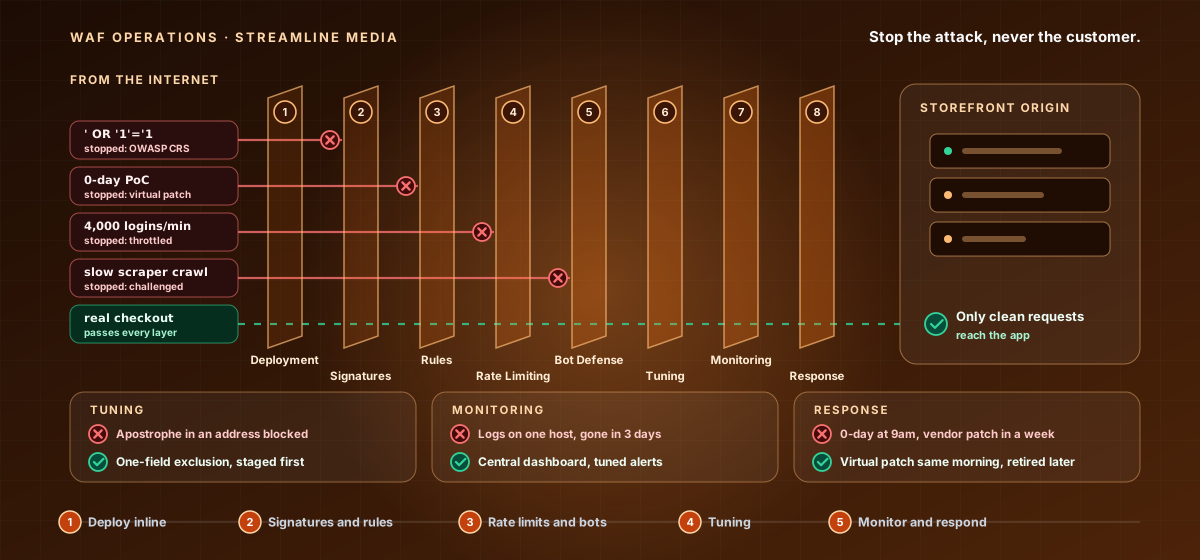
CY-MID-056Mid Level · WAF Operations
Web Application Firewall Operations — The WAF Defense Stack
A hands-on mid-level course that runs a WAF that blocks attacks without blocking customers. Work the WAF defense stack - eight layers: Deployment, Signatures, Rules, Rate Limiting, Bot Defense, Tuning, Monitoring, and Response - deploying managed and custom rules, cutting false positives, and stopping OWASP-class attacks and bots. Strictly defensive. Four hands-on activities in every lesson.
15 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Deploy a WAF in the right mode and topology for your apps.
- Tune managed and custom rules to block attacks with few false positives.
- Add rate limiting and bot defense without hurting real users.
- Monitor, alert, and respond to what the WAF sees.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.