← Back to catalogue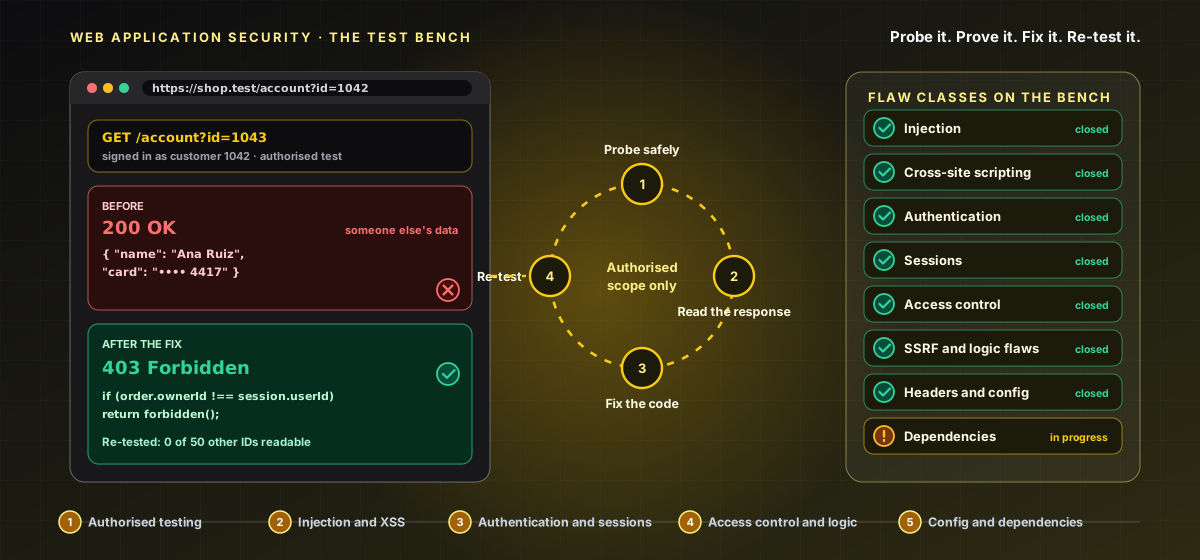
CY-SENIOR-015Senior Level · Web Security
Web Application Security — The Test Bench
A hands-on, senior-level course that tests and fixes web application vulnerabilities the professional way: probe a surface safely, read the response, then fix the code and re-test until the flaw is closed. Work every OWASP-class flaw — injection, XSS, broken authentication and access control, SSRF, and misconfiguration — on a real HTTP test bench with real requests and real remediation. Four hands-on activities in every lesson.
17 hours8 chapters32 lessons220 activities8 labs
What you'll learn
- Run the professional loop — probe safely, read the response, reproduce, fix the class at the code, re-test — under authorization.
- Find and fix injection and XSS with parameterization, safe APIs, and context-aware output encoding plus CSP.
- Harden authentication, sessions, and access control against enumeration, CSRF, IDOR, escalation, and mass assignment.
- Close SSRF, deserialization, upload, and misconfiguration flaws, and run the ongoing security-testing loop.
Price:৳10,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.