← Back to catalogue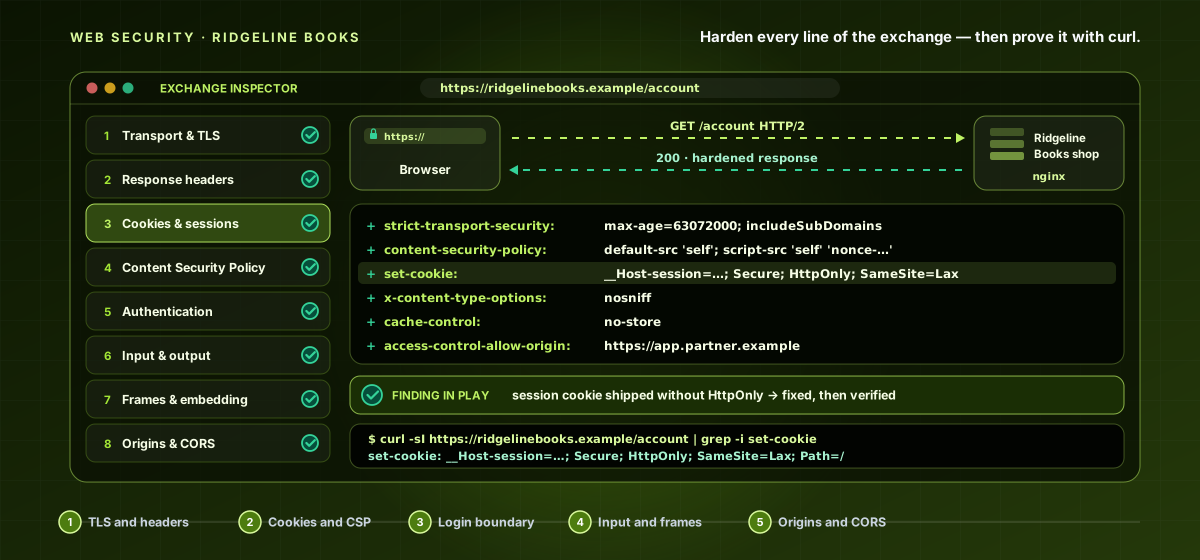
CY-MID-074Mid Level · Web Security
Web Security — Hardening the Exchange
A hands-on, task-first mid-level course that hardens a real web application one defense surface at a time. Work the exchange inspector across eight surfaces — TLS, headers, cookies, CSP, auth, input/output, framing, and origins — applying real nginx and app configs and proving every defense from the command line with genuine curl and openssl read-backs. Four hands-on activities in every lesson.
16 hours8 chapters40 lessons290 activities8 labs
What you'll learn
- Force HTTPS with HSTS, build the response-header shield, and lock down cookies with the __Host- prefix.
- Roll out a strict nonce-based CSP with Report-Only, and harden authentication end to end — hashing, throttling, WebAuthn, resets.
- Close injection structurally at every sink: validation, parameterized queries, context-correct encoding, and inert uploads.
- Contain frames and the supply chain, get CORS and CSRF right, and prove every defense from the console.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.