← Back to catalogue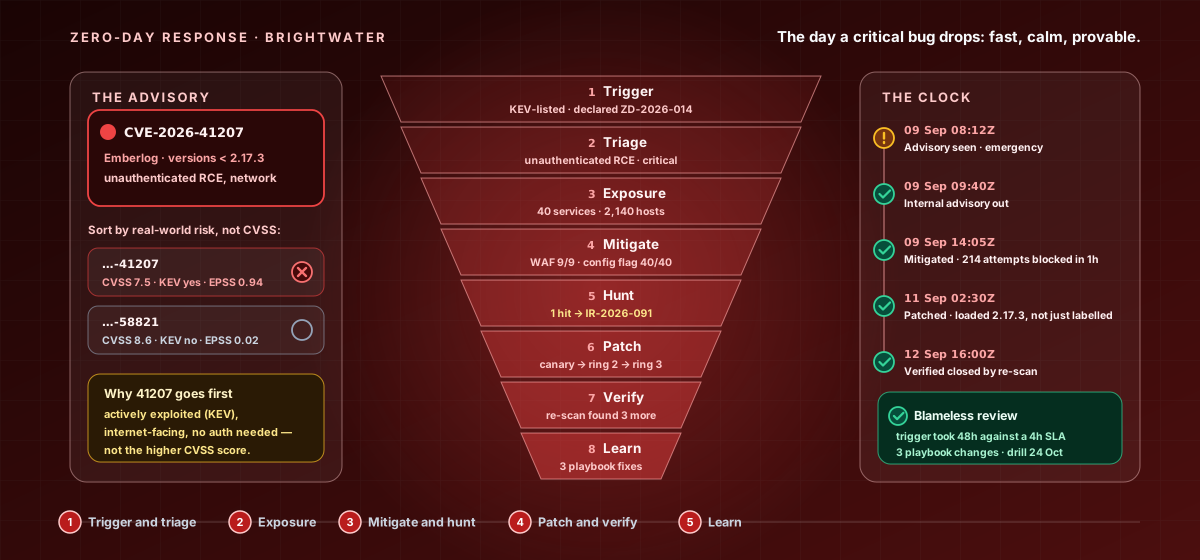
CY-MID-108Mid Level · Zero-Day Response
Zero-Day & Critical Vulnerability Response — The Emergency Funnel
A hands-on mid-level course that runs the emergency playbook for the day a critical, often actively-exploited vulnerability drops in software you already run. Work the emergency funnel across eight stages - Trigger, Triage, Exposure, Mitigate, Hunt, Patch, Verify, and Learn - responding fast on facts but proving closure, with real advisory intake, KEV/EPSS triage, SBOM/CMDB exposure sweeps, WAF and config mitigation, IOC hunting, expedited patch rollout, and re-scan verification. Four hands-on activities in every lesson.
15 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Watch every major advisory source and decide, fast and deliberately, what constitutes a real emergency.
- Triage a new critical advisory accurately using CVSS, KEV, and EPSS together, not severity alone.
- Sweep the whole estate for every affected instance and deploy compensating controls within hours.
- Hunt for prior exploitation, roll out the real fix through an expedited process, and verify closure by proof.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.